






Cookie-aware capture
Preserve public page state only when it changes the response
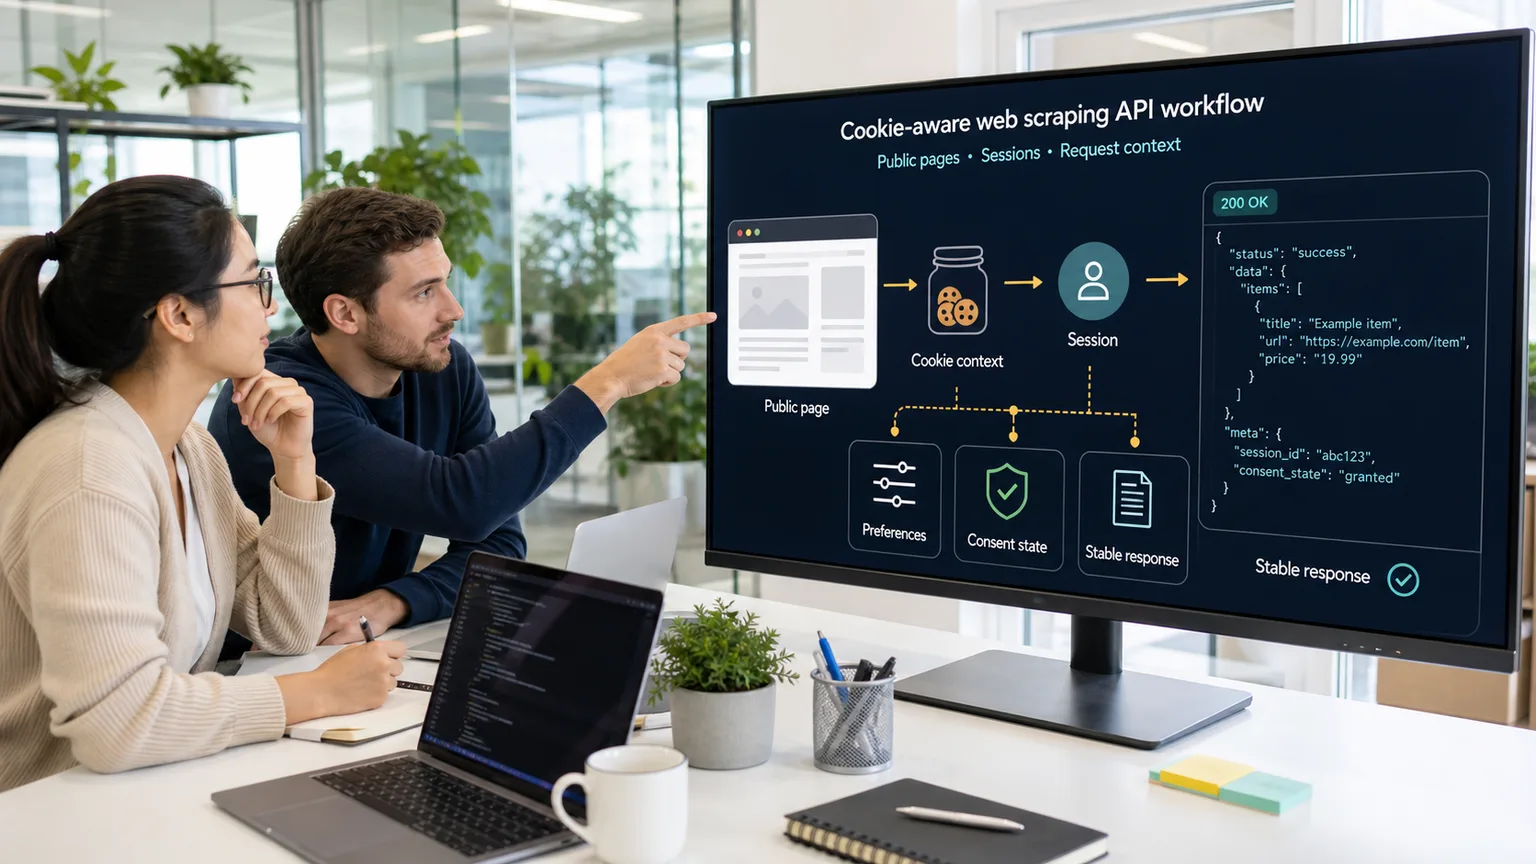
Cookies are useful when a public page remembers a lightweight state: consent, language, location hint, currency, preferences, or a previous step in a public browsing flow. ScraperFly gives teams a way to pass that context deliberately instead of making every scrape stateful by default.
The best cookie workflow starts simple. Fetch the page without state, inspect what changes when cookie context is present, and use sessions only when related requests must keep continuity. That keeps ordinary pages easier to debug and harder pages more predictable.
When do cookies matter for web scraping?
Cookies matter when the public response depends on state. A page may use cookies to remember consent choices, language, currency, region, display preferences, pagination state, or a lightweight workflow step. Without that context, the API may capture a banner, a default locale, a redirect, or a page variant that is not the one your product needs.
Cookies do not belong in every request. Many public pages return the same useful HTML, text, Markdown, metadata, screenshot, or PDF without any state. In those cases, a stateless request is cleaner: fewer moving parts, easier reproduction, simpler debugging, and less risk of confusing one target's requirements with the default profile for every target.
Practical takeaway: add cookies when they make the public response more accurate, not because stateful scraping sounds more powerful.
How are cookies different from sessions and headers?
Cookies are state values. Headers describe request context such as accepted language, content type, user agent policy, or referer when allowed. Sessions keep related requests using a consistent state context across time. A workflow can use one of these controls, combine them, or avoid all of them depending on what the public target actually requires.
The distinction matters because each control solves a different problem. If a target expects a language header, cookies may not help. If a route depends on a consent state, headers alone may not help. If a multi-step public workflow expects continuity, a one-off cookie value may be less reliable than a scoped session.
| Control | Use it when | What it should not become |
|---|---|---|
| Cookies | The public response changes because of consent, preference, locale, or state values | A blanket default for every target. |
| Sessions | Related public requests need shared continuity over multiple steps | A permanent state bucket for unrelated pages. |
| Headers | The target expects legitimate request context such as language or accepted content type | A copy of every browser header without purpose. |
| Rendering | JavaScript execution changes the useful page content | A substitute for missing cookie or session evidence. |
| Country routing | Public content changes by region, currency, availability, or redirects | A fix for state problems that are not geographic. |
How should teams test cookie-dependent pages?
Test three versions of the route. First, fetch the page without cookies and inspect the result. Second, fetch with the expected cookie context and compare final URL, status, response size, content type, visible fields, headings, and text. Third, use a session when the result depends on continuity from a previous public request.
This comparison keeps the workflow honest. If the useful content appears without cookies, keep the route stateless. If cookies remove a consent screen or preserve a legitimate preference, use them for that route class. If the state must carry across requests, use a session. If the page content is still missing because JavaScript builds it after load, test rendering separately.
For related controls, compare the web scraping API with sessions, custom headers scraping API, and JavaScript rendering API guides.
What are safe use cases for cookie support?
Cookie support is useful for public workflows where state improves accuracy without changing the legal or permission boundary of the target. Common examples include preserving a consent decision, keeping a selected language, maintaining a regional preference, keeping currency display consistent, continuing a public pagination flow, or avoiding repeated first-visit UI that hides otherwise public content.
It is not a shortcut into private data. Avoid using cookies to access account-only content, bypass authorization, or ignore target rules. ScraperFly is strongest when it helps teams fetch public pages with the right request context and clear evidence, while the application remains responsible for permissions and lawful use of collected data.
| Cookie use case | Why it helps | Production check |
|---|---|---|
| Consent state | Removes repeated consent UI from otherwise public content | Confirm the content is public and the consent state is appropriate. |
| Language preference | Keeps text and metadata in the expected locale | Compare with headers and final URL behavior. |
| Currency or region preference | Stabilizes public pricing or availability display | Check whether country routing also affects the response. |
| Public multi-step flow | Keeps continuity between related requests | Use scoped sessions instead of sharing state globally. |
| Pagination or filters | Preserves expected route state across related views | Make sure state does not leak across unrelated targets. |
When should cookies be avoided?
Avoid cookies when they do not change the response your workflow needs. Extra state makes debugging harder because two requests to the same URL may no longer be equivalent. It can also hide a simpler solution such as using raw HTML, choosing a better response format, adding an allowed language header, or narrowing the target route.
Avoid cookies when the target requires private access or an authenticated account that your workflow is not permitted to use. ScraperFly should be used for controlled public web workflows. If the data requires authorization, the right answer is not to smuggle state into the request; the right answer is to use an approved integration path or not collect that data.
How do cookies affect cost and reliability?
Cookies themselves are not usually the expensive part. Cost and complexity rise when a stateful workflow also needs sessions, rendering, waits, screenshots, PDFs, premium routing, or higher retry discipline. That is why the first question should be whether cookie context changes the captured public response enough to justify carrying state.
ScraperFly's flexible credit model helps teams test these decisions before scale. Use small tests to prove whether cookies, sessions, or rendering are required, then move recurring workloads to the credit path that fits the proven request profile. The pricing page and web scraping API credit cost calculator can help estimate the effect of heavier controls.
How does ScraperFly make cookie-aware scraping practical?
ScraperFly keeps cookie support inside the same API workflow as output formats, rendering, headers, routing, sessions, diagnostics, screenshots, and PDFs. Your team can test the target, inspect the difference state makes, and copy a canonical request once the correct profile is clear.
Use the API Builder to compare stateless capture with cookie-aware and session-aware requests. Keep simple pages on simple requests, use cookies for public state that matters, and reserve sessions for workflows where continuity is truly part of the target behavior.
Practical takeaway: cookie support works best when it is narrow, explainable, and tied to a public response difference your product actually needs.







